Home
 |
 |
 |
 |
 |
 |
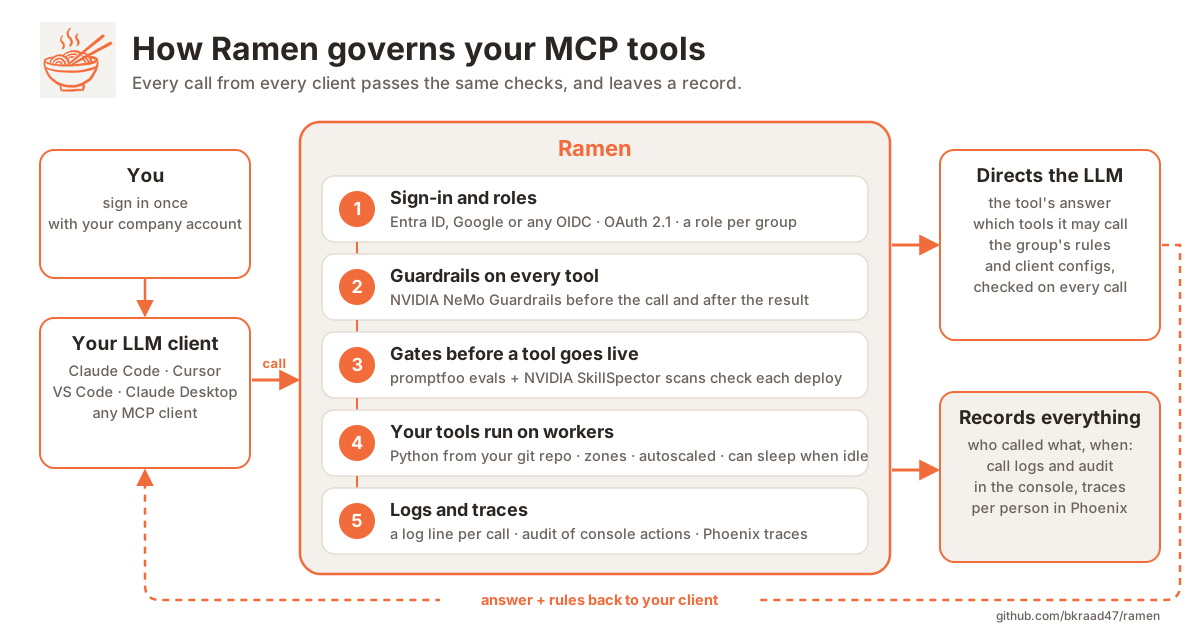
Governed MCP for teams. Ramen is a self-hosted MCP platform that enforces your organisation's security and structure on every tool call — the sanctioned home for your team's tools instead of shadow MCP servers on laptops. Your team keeps a git repo of tools, resources, prompts, apps and skills in plain Python. Ramen signs people in with a role per group, checks every call with guardrails (NVIDIA NeMo Guardrails, static and LLM-judged), gates every deploy with golden cases, promptfoo evals and an NVIDIA SkillSpector scan, and records every call — in the access log, the audit log and Arize Phoenix. It runs on a laptop or across zones on GKE, EKS and AKS, and speaks MCP 2026-07-28. You code in Python.
One project, three repositories — the server you install, the bridge your people run, and a group repo to copy.
Ramen · the server
ramen
What you install: the console, the Rust MCP node and the Python runtime, Helm charts and Terraform for GCP, AWS and Azure. Releases are tagged and built by CI.
Ramen · the client bridge
ramen-mcp-bridge
What your people run: pip install ramen-mcp-bridge, a stdio MCP server for
clients that cannot speak HTTP. Signs in through the console or carries a group key, keeps the group's policy and
writes its client configs. Bridge 1.0.0 is the bridge for Ramen 1.0.0: TLS by default, plaintext only with an
explicit --insecure for local development.
Ramen · the demo group
ramen-demo-mcp
What you copy: the group repo every guide deploys — tools (one asks before it acts, one runs as a task, Iris data tools), resources, prompts, an MCP App, skills, golden cases, NeMo rails, promptfoo evals and LLM configs.
Why teams pick it
- Sanctioned MCP, not shadow MCP. Tools in a repo you review, on your cluster, answering only people who signed in with your identity provider and hold a role in the group.
- No eval, no deploy. A canary first; golden cases always, promptfoo evals and a SkillSpector scan when the engines are on, and a group admin can make either stop the deploy.
- Guardrails per tool, not per chat. Rails run inside the worker for every client, before the tool and after it.
- Every tool call has a name. A person's sign-in or a named key on every call; access log, audit log, Phoenix.
- It directs the LLM. The group's rules and client configs are versioned, accepted per person and checked on every call.
- Scales for what you need now, and follows MCP's 2026 direction: stateless requests, tasks, multi round-trip requests, MCP Apps and Skills over MCP.
Built-in governance and dev tools
| Tool | What it does in Ramen | Where it runs |
|---|---|---|
| NVIDIA NeMo Guardrails | rails per tool, before the call and after the result | in every worker, on the laptop too |
| promptfoo | the repo's eval suite against the canary on every deploy | a Job in the cluster |
| NVIDIA SkillSpector | scans the repo's skills and the served tools on every deploy | a Job in the cluster |
| Arize Phoenix | traces, one project per group, the person on every span | next to the console, and on the laptop |
Key features
The protocol
- MCP 2026-07-28 next to 2025-06-18 on one endpoint, per request: stateless requests, standard headers,
server/discover, subscriptions (Transport). - Tasks, multi round-trip requests (elicitation, sampling, roots), progress, completion.
- MCP Apps (
ui://) and Skills over MCP (skills/list,skill://) from folders in the repo. - Streamable HTTP and gRPC on one port, one set of guards; a stdio bridge for every other client.
Quality and safety gates
- Canary deploys with a schema compatibility gate and golden cases.
- promptfoo evals from the repo, run on every deploy, report or gate per group.
- NVIDIA SkillSpector scans of the repo's skills and the served tools, with a report page.
- Guardrails in the worker: NeMo rails, static or LLM-backed, or your own
policy.py.
Enforced on every sign-in
- Client policies: telemetry, evals, scans, LLM configs and guardrails carry versions every call must hold
(
-32024…-32029), on every sign-in path and every client. - LLM configs from the repo, accepted per person and version, written to their tools by the bridge.
- Telemetry by group and user: one Phoenix project per group,
ramen.useron every span, client telemetry through the console's OTLP ingest. - LLM judge proxy: provider keys never leave the console.
Run it
- GCP, AWS and Azure from Terraform and Helm; optional Phoenix, promptfoo and SkillSpector with one switch each.
- Roles per group (Super admin, Group admin, Viewer, MCP user, custom roles), Entra ID and Google Workspace.
- Autoscaling by Ramen on load and latency; sleeping workers; Redis throttling.
- Per-group image builds on deploy; satellite clusters for zones in other regions.
- TLS on every hop with a per-install CA; plaintext refused on cloud installs.
What is verified. The 1.0.0 release candidate ran live on GKE (with a satellite cluster), EKS and AKS: a demo deploy with evals 6 passed and a SkillSpector SAFE verdict, a tool call through each load balancer, the full verification suite and load tests with p95 under 1.5 s on all three, after two independent security passes on GKE; what each covered and what is open: Transport → What is verified and the Threat model. Everything else is in the wiki; to let a coding agent deploy and run it, install the agent skills.
Fork it, shape it, talk to us
Ramen is BSD-3-Clause and made to be forked: copy the demo group repo for your own tools, or fork Ramen and change it for your organisation. Collaboration is welcome — questions, ideas and what you built go to GitHub Discussions; how changes get in is in Contributing.